Cisco has identified rising operational vulnerabilities as shadow AI risks continue to challenge enterprises across Saudi Arabia. Employees increasingly use unauthorized generative artificial intelligence tools to handle daily tasks and accelerate output. However, deploying these third-party applications without centralized administrative oversight exposes corporate databases to severe data leaks.
Financial Repercussions of Unregulated Applications
Recent market research cited by Cisco demonstrates substantial commercial damage when employees bypass internal IT protocols. Organizations with elevated exposure to shadow AI risks reported security breach remediation expenses averaging $670,000 higher than businesses maintaining rigorous software oversight.
In addition, research showed that 97% of enterprises that suffered an artificial intelligence security incident operated without established access permissions. The findings reflect growing vulnerabilities as automated models handle proprietary records without supervisory tracking.
Executive Perspectives on Workplace Governance
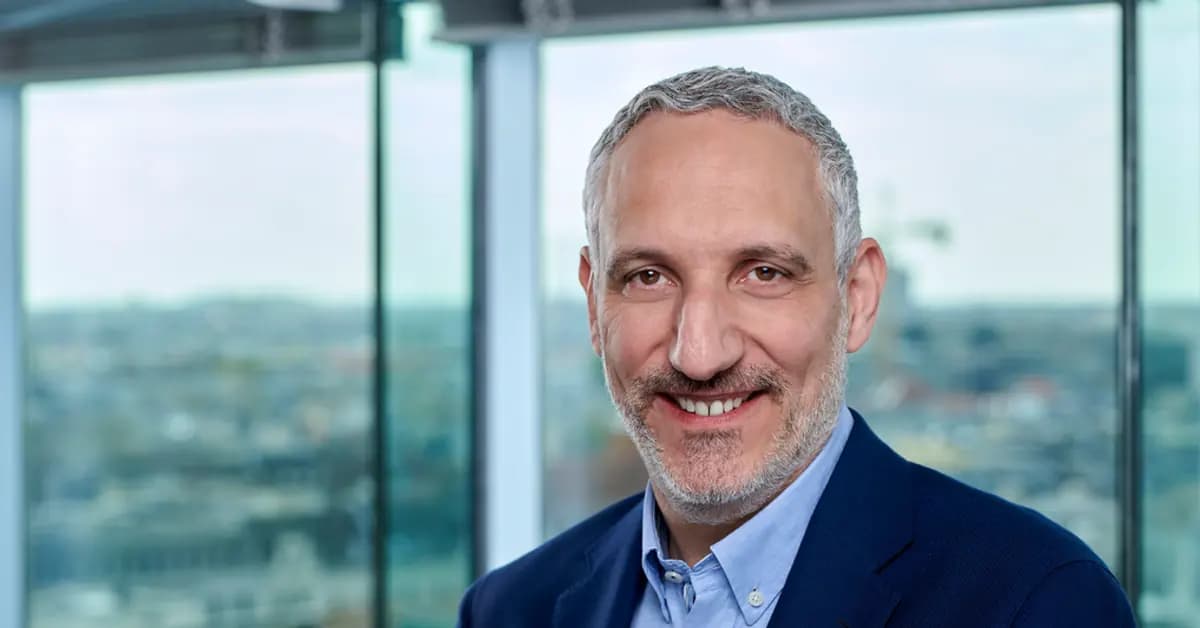
Fady Younes, Managing Director for Cybersecurity at Cisco Middle East, Türkiye, Africa, Caucasus and Central Asia (METAC), addressed the shifting operational landscape during a briefing in Riyadh.
“AI is helping businesses work more efficiently and unlock new opportunities. However, without the right security measures, unauthorized AI tools can expose sensitive data and create risks that organizations may not be aware of. Businesses need clear policies, strong access controls and better visibility into how AI is used. This will help them protect their systems while allowing employees to use AI safely and effectively.”
Fady Younes, Managing Director, Cybersecurity, Cisco METAC
Three Priorities to Manage Shadow AI Risks
To assist security leaders in maintaining data confidentiality, Cisco published three practical guidelines designed to balance operational progress with defense requirements.
- Improve visibility into AI usage: Identify and monitor all AI applications running within the corporate network, including personal accounts and web browser add-ons.
- Strengthen access controls and data protection: Restrict employee access to sensitive information and verify that systems process only the parameters required for assigned tasks.
- Establish clear AI governance policies: Introduce direct guidelines supported by scheduled risk reviews while supplying workers with vetted, secure software.
Building Resilient Operations for the Future
Corporate leaders need not slow technical advancement to protect company assets. Instead, providing verified enterprise tools diminishes employee reliance on external, unmonitored platforms.
Saudi organizations can safeguard digital assets by treating governance as an essential element of modern corporate strategy. Consequently, addressing shadow AI risks directly enables firms to adopt automation safely while protecting sensitive enterprise data across the digital economy.