A widespread global Microsoft outage disrupted services for millions of users worldwide starting on Thursday, November 12, 2026. The incident interrupted vital business systems and brought email communications to a standstill before systems slowly began recovering, according to an academic commentary note from the Institute for Cyber Security at City St George’s, University of London, a cybersecurity research institute.
While Microsoft reported gradual improvements and email queues approaching normal operating levels, many organizations remained affected. The event highlighted the systemic vulnerabilities created when businesses worldwide depend on a concentrated pool of cloud vendors.
The Impact of the Global Microsoft Outage
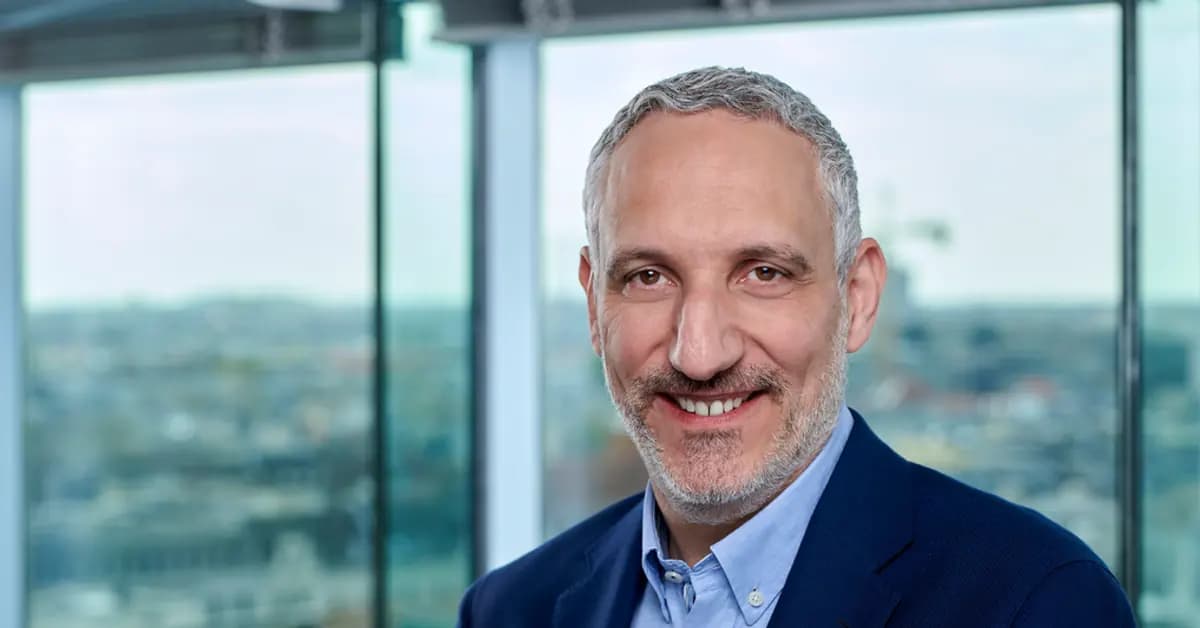
Professor Raj Rajarajan, Director of the Institute for Cyber Security at City St George’s, University of London, addressed the wider consequences of the incident in a written note. He observed that service interruptions carry heavy operational costs across critical industries.
“This Microsoft outage remains a powerful illustration of the risks of relying on a small number of technology providers and the significant economic consequences of large-scale service disruptions.”
Professor Raj Rajarajan, Director of the Institute for Cyber Security at City St George’s, University of London
According to the commentary, modern business models increasingly concentrate operational risk inside a few large corporate networks, heightening potential economic consequences during unexpected technical failures.
Rising Demands from Artificial Intelligence
The growth of artificial intelligence applications is placing additional stress on existing enterprise networks. Professor Rajarajan wrote that legacy digital systems were not built to manage the intensive computational needs of modern intelligent platforms.
Enterprises need scalable computing resources to handle volatile processing requirements. Because industry experts are still learning how to forecast workload patterns, similar capacity challenges are likely to emerge over the next 12 to 15 months, according to the note.
Emerging Attack Surfaces and Threat Vectors
System expansions also introduce significant cybersecurity complications. Integrating machine learning tools into operational workflows expands the surface area available to malicious actors, creating entry points that attackers can exploit before software developers discover them.
“AI systems introduce new and evolving attack surfaces, creating opportunities for threat actors to identify and exploit previously unknown vulnerabilities.”
Professor Raj Rajarajan, Director of the Institute for Cyber Security at City St George’s, University of London
Consequently, the potential disruption grows more severe as autonomous capabilities become deeply embedded within essential utility and enterprise operations, according to the author.
Strategies for Digital Redundancy
To counter these systemic risks, Professor Rajarajan recommended that organizations adopt multi-vendor deployment strategies and invest in sovereign hardware and software assets. Dividing operations among multiple independent vendors prevents an isolated failure from paralyzing an entire institution.
The note concluded that institutions must build automated fail-safe architectures capable of transferring operational workloads across different providers instantly. Establishing structural redundancy will remain essential to maintain financial and operational stability following the recent global Microsoft outage.