AI-generated illustration
The Federal Bureau of Investigation is probing an alleged FBI data breach after the cybercriminal group ShinyHunters claimed responsibility for accessing recruitment systems. According to Ars Technica, the hackers claim to hold between two and three terabytes of sensitive records detailing thousands of current agents, former staff, and job applicants.
Scope of the Alleged FBI Data Breach
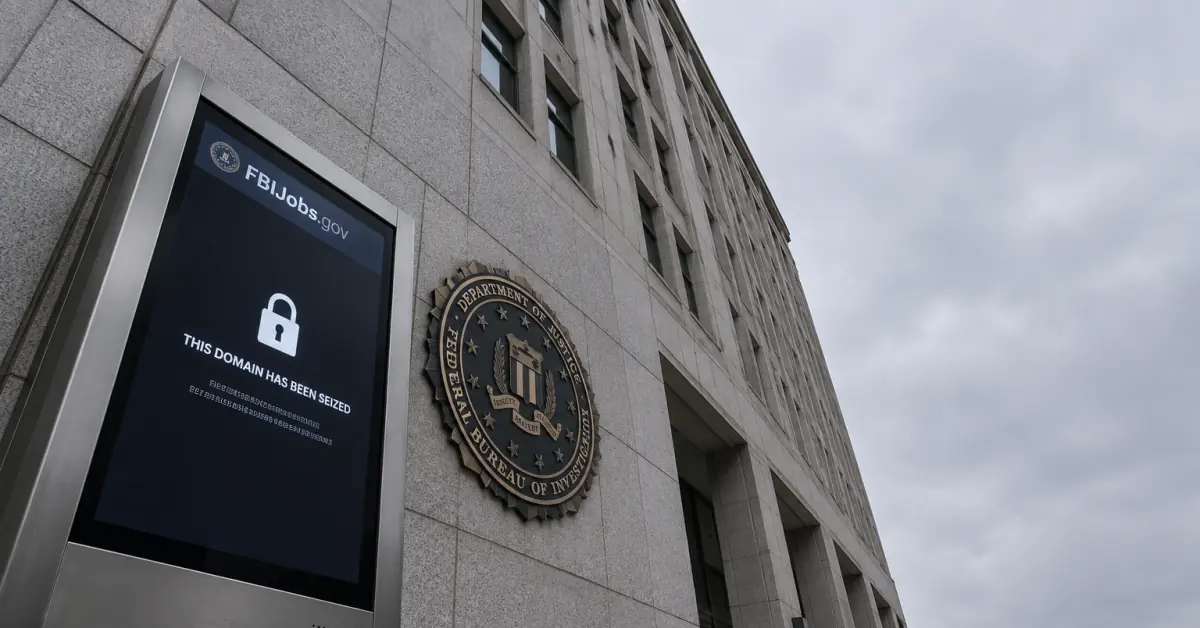
The threat group posted a seizure banner on the agency recruitment portal, FBIJobs.gov, before the portal became unavailable. Stolen information reportedly includes names, home addresses, phone numbers, spousal details, and medical records. In addition, reporting by Bloomberg indicates the files could contain sensitive details regarding counterintelligence assignments focused on foreign nations and gang investigations.
Zero-Day Exploit and Cloud Infrastructure
The intruders stated that they weaponized a zero-day flaw in Oracle PeopleSoft software, which human resources departments commonly deploy. After gaining initial access, the attackers reportedly moved into an Amazon hosted government cloud environment storing applicant information. The incident has raised major concerns regarding cybersecurity standards across critical infrastructure, as federal agencies evaluate third-party software risks.
Investigators continue assessing the digital perimeter to understand whether the intrusion occurred via vendor software or enterprise networks. The verification process remains active while officials work to evaluate how deeply an FBI data breach might have impacted internal systems.
Stated Motives Behind the Incident
ShinyHunters claimed the operation was not financially motivated and did not demand a monetary ransom. Instead, the hackers demanded that federal leadership modify a public advisory published earlier in the year. The group addressed messages directly to agency director Kash Patel and cyber division leadership, demanding retractions regarding past law enforcement statements.
Official Response and Protective Measures
The agency notified employees internally to adopt security precautions while technical reviews continue. Representatives confirmed they are actively investigating unauthorized activity related to the portal alongside external service providers. Meanwhile, security analysts note that foreign intelligence entities could potentially exploit personal personnel records if the stolen files leak publicly.
This incident represents a notable challenge for federal network administrators in an era of complex software dependencies. As technical teams audit database perimeters, the full extent of the reported FBI data breach remains the primary focus of active forensic inquiries.