ClickFix malware attacks are expanding across personal computers running Windows and macOS systems, according to reporting by TechCrunch. Security analysts warn that these deceptive campaigns trick victims into executing harmful commands directly in their computer terminals.
How ClickFix Malware Attacks Target Operating Systems
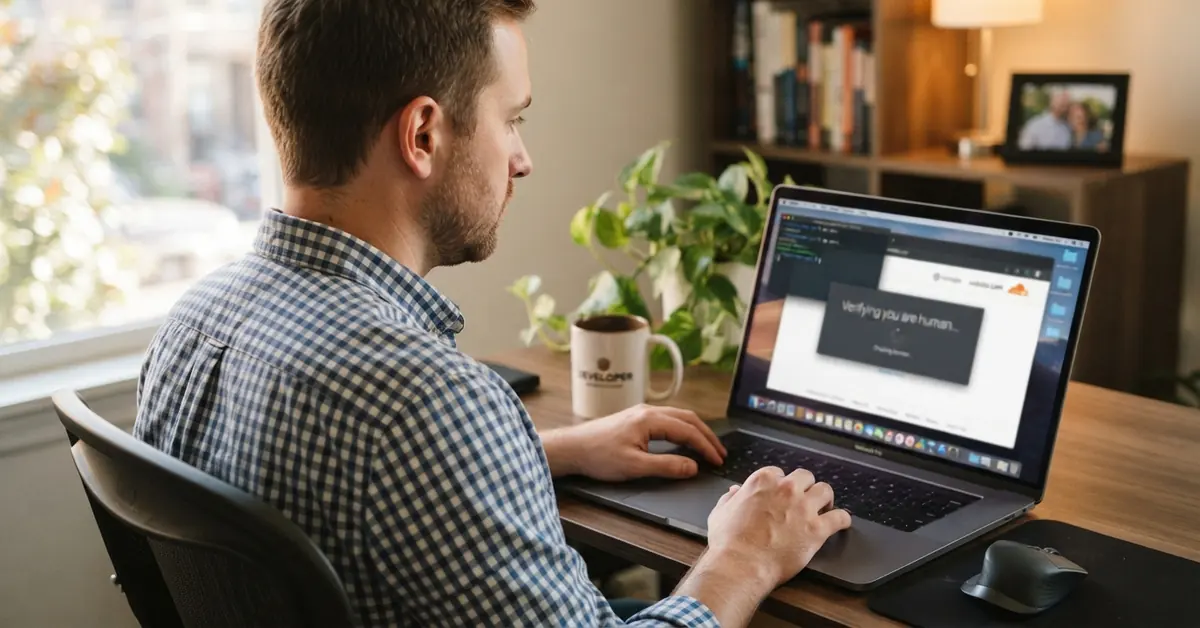
The threat begins when an unsuspecting user visits a compromised website or clicks a malicious online advertisement. Victims encounter a fake verification window that mimics legitimate anti-bot checks, such as Cloudflare interfaces. When clicked, the prompt presents instructions asking the user to copy a line of code and paste it into Windows PowerShell, the Run dialog, or the macOS Terminal app.
Executing these commands delivers info-stealing malicious software directly to the device. Consequently, malicious actors gain immediate access to stored browser credentials, active session tokens, and cryptocurrency wallets. Because the execution occurs within the built-in system shell, the technique bypasses several standard endpoint security defenses.
Compromised Ad Accounts on Social Platforms
Recent investigations revealed that attackers compromised an official Max advertising account on social media network Reddit. Hackers utilized the access to distribute fake advertisements linking directly to deceptive landing pages. A representative from Reddit confirmed the incident, stating that the platform locked the compromised profile and removed the malicious advertisements.
Security firm Netskope observed extensive infrastructure supporting these operations, detecting approximately 5,400 connected websites. Meanwhile, research teams noted that some campaigns employ public Google Sheets or decentralized blockchain contracts to control the spread of ClickFix malware attacks.
Enterprise Impact and Security Defense Strategies
The shift toward technical terminal deception simplifies the delivery pipeline for attackers by eliminating the requirement for signed application installers. In response, IT administrators can restrict terminal and command prompt utilities across domain-connected computers to mitigate corporate exposure.
For personal devices, specialized endpoint tools such as BlockBlock for macOS intercept attempts to establish persistence upon command execution. Security researchers emphasize that regular software updates and heightened user vigilance remain crucial lines of defense.
Future Outlook for Computer Users
Organizations tracking global cybersecurity incidents indicate that automated verification lures will persist as long as users face friction with legitimate CAPTCHA prompts. Raising technical awareness across workforces ensures individuals avoid running untrusted terminal scripts.